File Path Traversal Simple Case
title: “Path Traversal – Unauthorized File Access via Directory Traversal | Simple Case” date: 2026-03-29 14:00:00 +0530 categories: [A02 - Security Misconfiguration, Path Traversal] tags: [ path...
title: “Path Traversal – Unauthorized File Access via Directory Traversal | Simple Case” date: 2026-03-29 14:00:00 +0530 categories: [A02 - Security Misconfiguration, Path Traversal] tags: [ path...
🧠 Overview This lab demonstrates a privilege escalation vulnerability where user roles are controlled via client-side input. By modifying a cookie value, an attacker can escalate privileges and g...
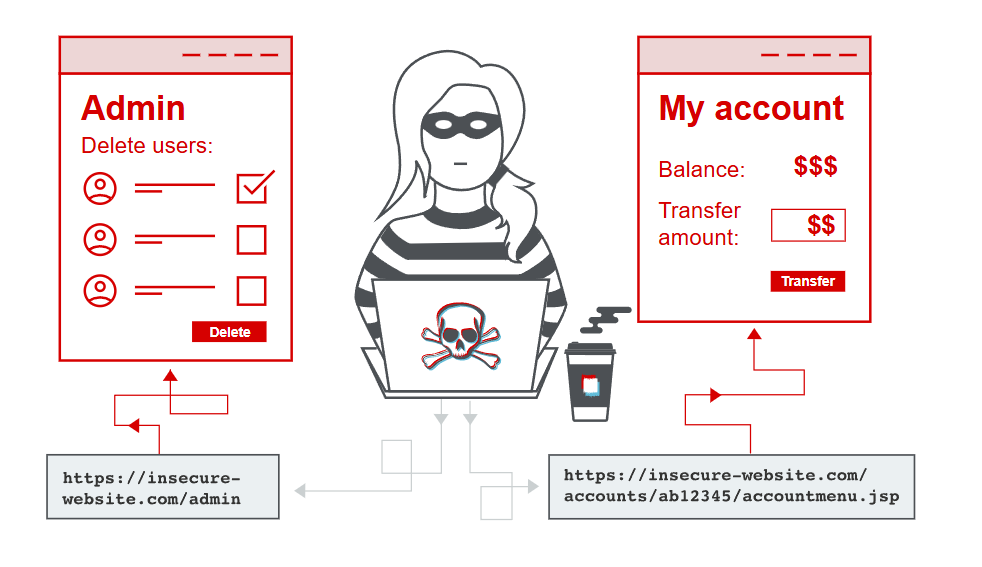
🧠 Overview This lab demonstrates why security through obscurity is ineffective. Even when administrative endpoints use unpredictable URLs, they can still be exposed through client-side code such ...
Overview This lab demonstrates a classic case of broken access control, where sensitive administrative functionality is exposed without authentication. An attacker can directly access privileged ...
Overview This lab focuses on performing a complete network penetration testing workflow, starting from reconnaissance to exploitation. It highlights weak authentication mechanisms in an FTP service...